
architecture
The Enterprise Case for VCF
Run AI, containers and virtual machines on one platform, on hardware you already own. What that adds up to, and what to plan around.
architecture
Run AI, containers and virtual machines on one platform, on hardware you already own. What that adds up to, and what to plan around.
security
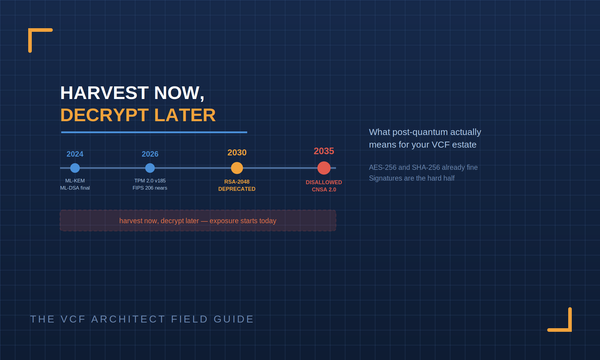
RSA-2048 gets deprecated in 2030 and disallowed in 2035. That's closer than it sounds when the migration touches Secure Boot, TPMs, code signing and every certificate authority you run. Here's the honest position, including the parts that don't need fixing.
security
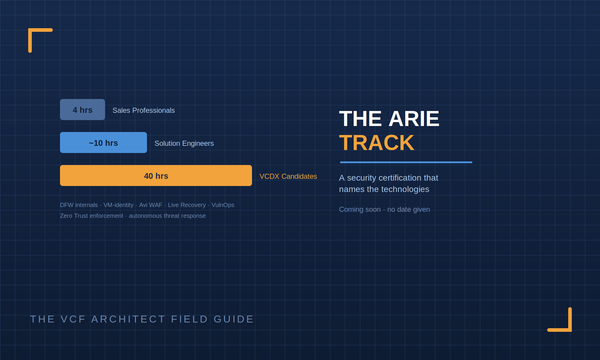
Three paths, forty hours at the deep end, and a curriculum list specific enough to tell you what Broadcom thinks a hardened VCF estate looks like. Useful even if you never sit the exam.
security
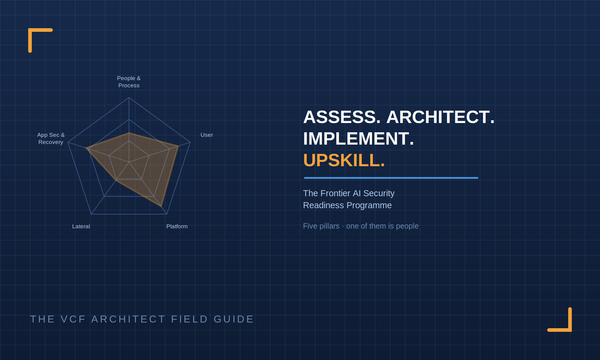
A four-stage security framework with a scored assessment underneath it. The interesting part isn't the programme, it's the five pillars it scores you against, and the fact that one of them is people.
security
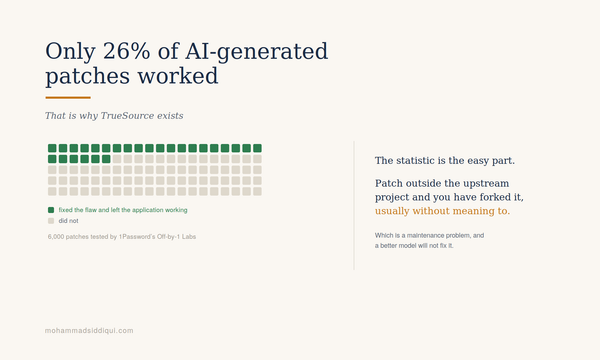
Six thousand AI-generated patches were tested. A quarter of them fixed the vulnerability without breaking the application. The statistic is the easy part.
events
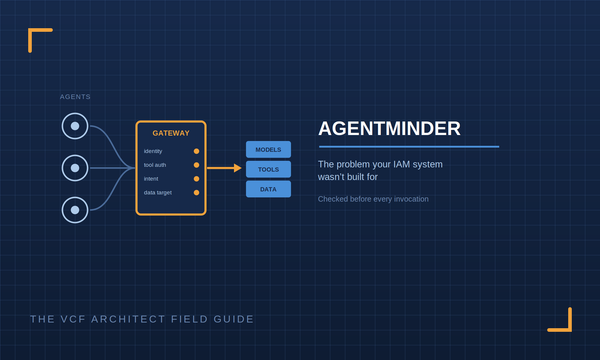
An autonomous agent doesn't fit the user model or the service account model. Broadcom's answer gives agents identities, missions and runtime policy, and routes every action through a gateway that checks intent before execution.
operations
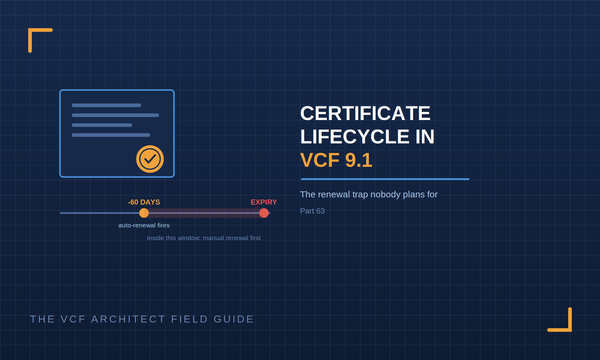
Auto-renewal in VCF 9.1 fires 60 days before expiry, which sounds like plenty of margin until you find out you can't switch it on for a certificate that's already inside that window. Here's how the renewal model actually works and what to
Newsletter
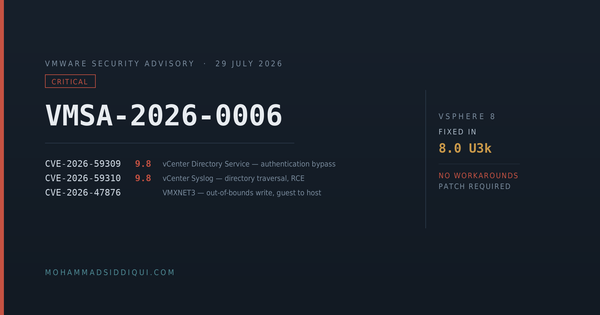
The 29 July advisory reaches vSphere 8: ESXi 8.0 U3k resolves CVE-2026-47876 live-patchable and vCenter 8.0 U3k closes two more.
Newsletter
Five CVEs resolved across ESX and vCenter under VMSA-2026-0006, released 29 July. The detail that matters operationally: the ESX patch applies without reboot or evacuation
Newsletter
The same 29 July advisory that patched three components on 9.0.2 asks exactly one thing of VCF and VVF 9.1 estates: vCenter 9.1.0.0300, resolving CVE-2026-59310.
Newsletter
Broadcom’s July post on Security Technical Implementation Guides lands squarely in defence territory but the compliance-as-operations model it describes is exactly where APRA and DORA are heading.
Newsletter
Intel TDX and AMD SEV-SNP reach general availability, Quick Boot returns on CC-active hosts, and VCF Operations profiles host capability automatically.