A customer asked me a few months back what it would cost to add database monitoring. We went through it, and about ten minutes in it became clear they already had it. Entitled, not deployed, nobody had looked.
That is not unusual. It happens because entitlements change at renewal, deployments change on project boundaries, and the two almost never get reconciled. So capability arrives quietly and sits there.
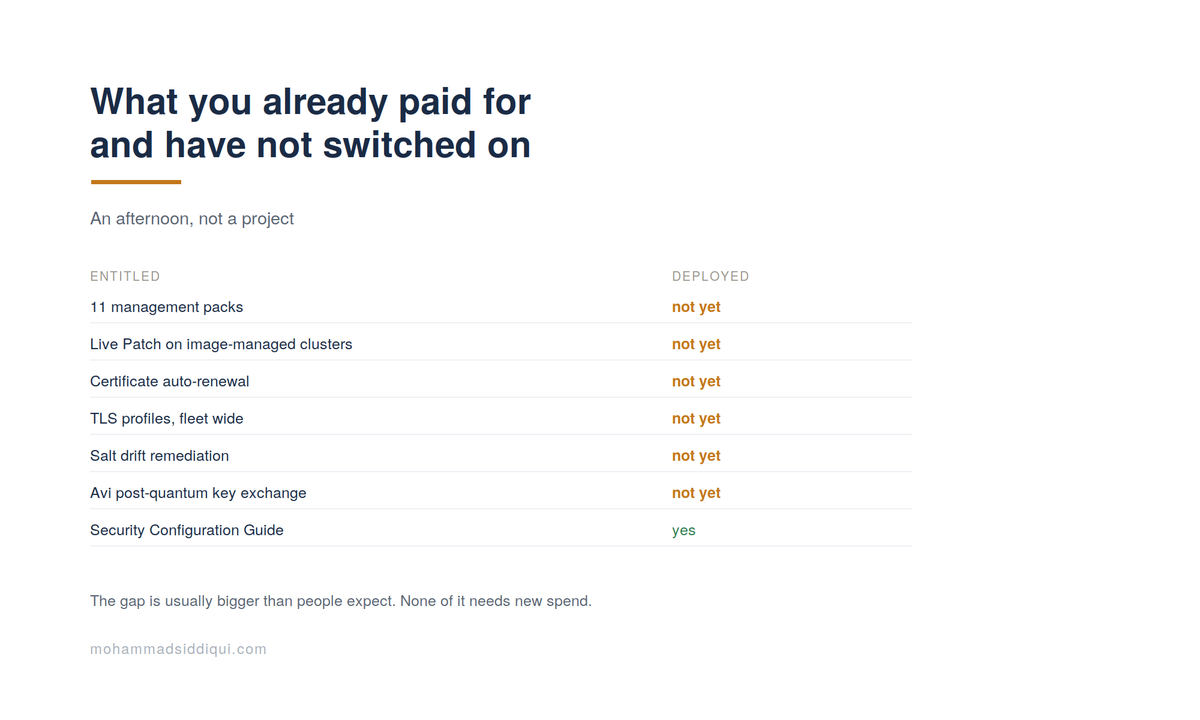
Here is the list I'd work through. None of it needs new spend. Some of it needs an afternoon.
One caveat up front
Editions differ, and several things below are VCF or VCF Edge only rather than vSphere Foundation. I've flagged which. Check your own entitlement against the feature comparison before you get excited about any particular line.
Monitoring you probably already own
Management packs, eleven of them
Five are databases: SQL Server, Oracle, PostgreSQL, MySQL and MongoDB. Two cover infrastructure reach, Network Devices and SNMP. Three are platform and integration, ServiceNow, Orchestrator and Aggregator. One is Kubernetes. They all reached GA at 9.1.1, rebuilt to carry log content as well as metrics because log management converged into VCF Operations. Infrastructure packs are available across editions. The application and database ones are VCF or VCF Edge only, which is the boundary that catches people. Packs are on the marketplace and the convergence detail is in the Operations for Integrations release notes.
Log management, now in the same place as metrics
If you're still treating logs and metrics as separate products with separate content libraries, that gap closed. During an incident it means one place to look rather than two, which is worth more than it sounds at 2am. Legacy content packs can be converted rather than rewritten.
The AI Assistant in the Operations console
Arrived in 9.1.1. Day 2 troubleshooting and diagnostics, and the part that matters for regulated customers is that you can point it at a model you host yourself rather than sending operational data out. Detail here.
OpenTelemetry observability for VKS
Also 9.1.1. If you run VKS and have ever tried to troubleshoot something that appeared and vanished inside ninety seconds, this is the gap it fills.
Lifecycle and patching
Live Patch, if your clusters are image-managed
This is the one I'd check first. Live Patch is the fast route for security patching, and it requires image-managed clusters. Plenty of estates upgraded and left clusters on baselines, which means the capability is entitled, present, and unavailable. Converting is not difficult. It's just never urgent until the week it is.
Certificate automation
Auto-renewal exists and is off in a lot of places. Worth knowing it fires 60 days before expiry and cannot be enabled for a certificate already inside that window without renewing by hand first. Management and instance certificates configure separately. Documentation here.
TLS profiles
Set, apply and audit TLS configuration across the fleet rather than host by host. Turns crypto configuration from a per-host setting into a managed property, which is also the groundwork for post-quantum work later.
Salt for drift remediation
Continuous compliance monitoring and drift correction. Most people who have it are not using it. Start in detection mode and look at what it finds before you let it change anything.
Security you may not have enabled
Post-quantum key exchange in Avi
Avi Load Balancer already supports hybrid post-quantum key exchange in TLS. If you have public-facing services behind Avi, you can protect them against harvest-now-decrypt-later today, with no waiting for standards or hardware. Configuration guide. This is the most actionable security item on the whole list and hardly anyone has switched it on.
The Security Configuration Guide and STIG readiness content
Free, published, and more thorough than most internally written hardening standards. If your security baseline was written for 6.7 and patched since, it is worth reading the current guide end to end. Here.
vDefend capabilities you already licensed
Distributed firewall, IDS/IPS, and in 9.1.1 the agentic discovery features including shadow AI detection. Worth running discovery even if you do nothing else with it, because the inventory of what is talking to what usually contains surprises.
Platform capability sitting idle
VCF Automation, if you have it and are not using it
A lot of estates have the entitlement and run everything through tickets anyway. That is the largest single gap between what people pay for and what they use. It is also the hardest to close, because it is an operating model change rather than a deployment. Worth a separate conversation rather than an afternoon.
Data Services Manager
Database provisioning as a service. Databases provisioned through DSM get monitoring automatically with no manual configuration, surfaced in a Data Services view. If you have DSM and are hand-building databases, that is effort you are choosing to spend.
GitOps with Argo CD
Native in VCF Automation from 9.1.1, Tech Preview. Worth knowing about and understanding the constraints, one instance per hosting namespace scoped to a single region, but not worth building on yet. Detail here.
How to actually do the audit
An afternoon, not a project.
Why the slide matters
Entitled but not deployed is the clearest budget conversation you will ever have. It costs nothing to close, it shows the platform investment working, and it makes the case for the next phase far better than a feature list does. Keep it to one page and update it quarterly.
Want a score rather than a reading list?
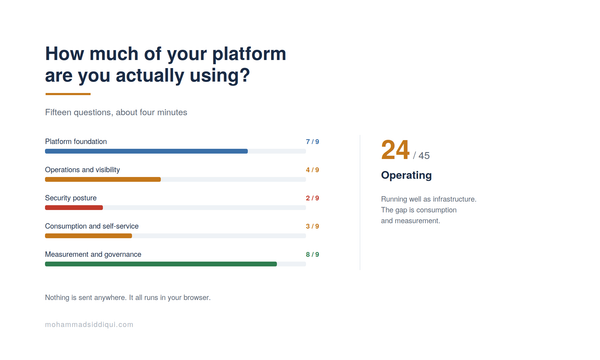
I built a short self-assessment covering the same ground. Fifteen questions, about four minutes, and it scores your estate across five areas with what I would do next in each. Nothing is sent anywhere, it all runs in your browser.