Regulator Control Map
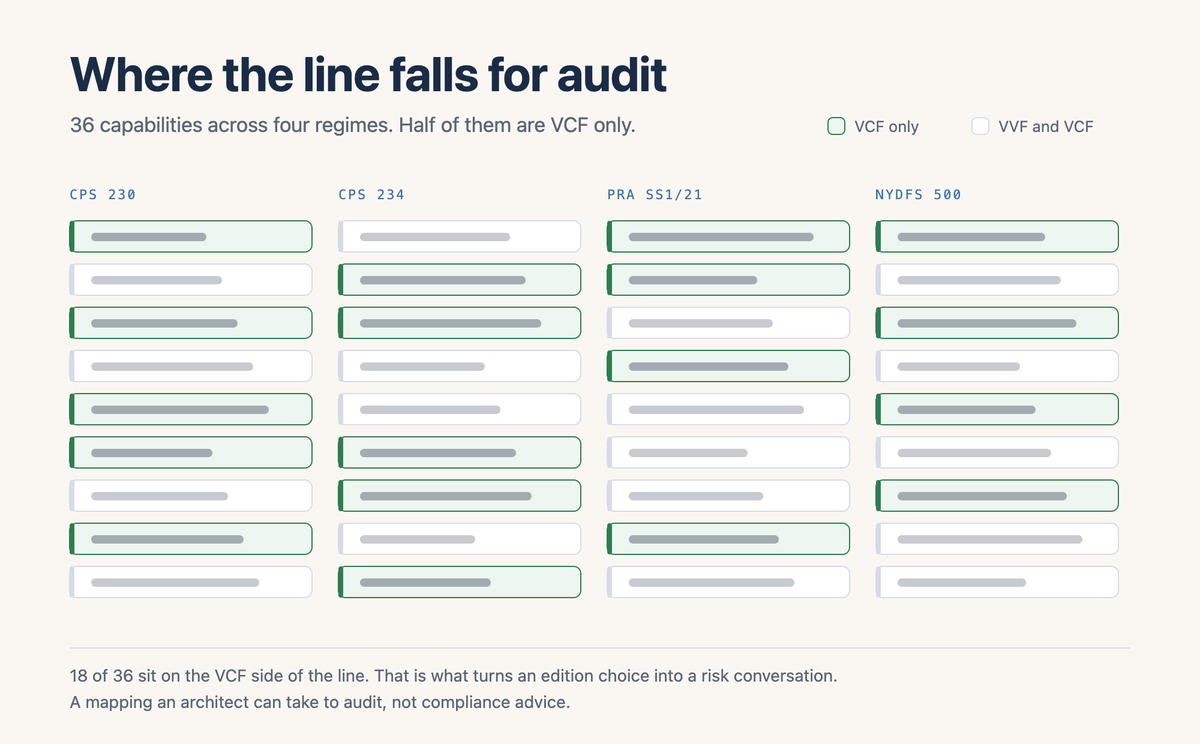
CPS 230, CPS 234, PRA SS1/21 and NYDFS Part 500 control areas mapped to the VCF and VVF capabilities that help evidence them, and what evidence to collect. An architect's mapping, not compliance advice.
Runs entirely in your browser. Nothing you enter is sent anywhere.
Which regimes apply to you
Use this with the design, not instead of it. Edition Fit Check tells you whether the capabilities below are even in the edition you are buying. Several of them sit on the VCF side of the line.
Read this before you use any of it
- This is an architect's mapping, not compliance advice. It lines up control areas with the platform capabilities that help you evidence them. It is not legal advice, it is not an attestation, and no platform makes anyone compliant with anything.
- Your obligations are set by your regulator and your own risk framework, not by a vendor's feature list. Treat this as a starting point for the conversation with your risk and audit functions, and expect them to add to it.
- Control references are indicative. Paragraph numbering and emphasis change as standards are revised. Check the current text of the standard that applies to you.
- Capability is not evidence. Having NSX does not evidence segmentation. The exported policy, the test result and the change record do. The right-hand column is what you would go and collect.
Checked 7 November 2026
Capability mapping checked against Broadcom documentation on 7 November 2026, against VCF 9.1.1. The control areas are an architect's reading of the standards, not a legal interpretation, and the standards themselves are revised on their own cadence. Check the current text of whichever standard applies to you.
Where this comes from
- Edition Fit Check, which tells you whether the capabilities mapped here are even in the edition you are buying.
- APRA Prudential Standard CPS 230, Operational Risk Management, and CPS 234, Information Security, as published by APRA.
- PRA Supervisory Statement SS1/21, Operational Resilience, as published by the Bank of England.
- NYDFS 23 NYCRR Part 500, Cybersecurity Requirements for Financial Services Companies, as published by the New York State Department of Financial Services.
- Broadcom product documentation for the capability side of the mapping. Regulator texts are not linked here because the canonical URLs move between revisions; go to the regulator's own site for the current version.
What this tool cannot know
- Your obligations. These are set by your regulator and your own risk framework, not by a vendor feature list or by this page.
- Whether a capability you hold is configured in a way that actually evidences anything. Having the product is not the control.
- Paragraph numbering. Control references are indicative and standards get revised.
- Anything outside the platform. Most of a CPS 230 response is process, people and third parties, none of which appear here.
- Whether your auditor will accept any of it. That is a conversation, and this is a starting point for it.
Part of the VCF planning toolkit
Next, see what the management plane will cost in worker nodes once you are on 9.1.